By maxaeo.ai | Published 2026-10-13 | Updated 2026-10-13
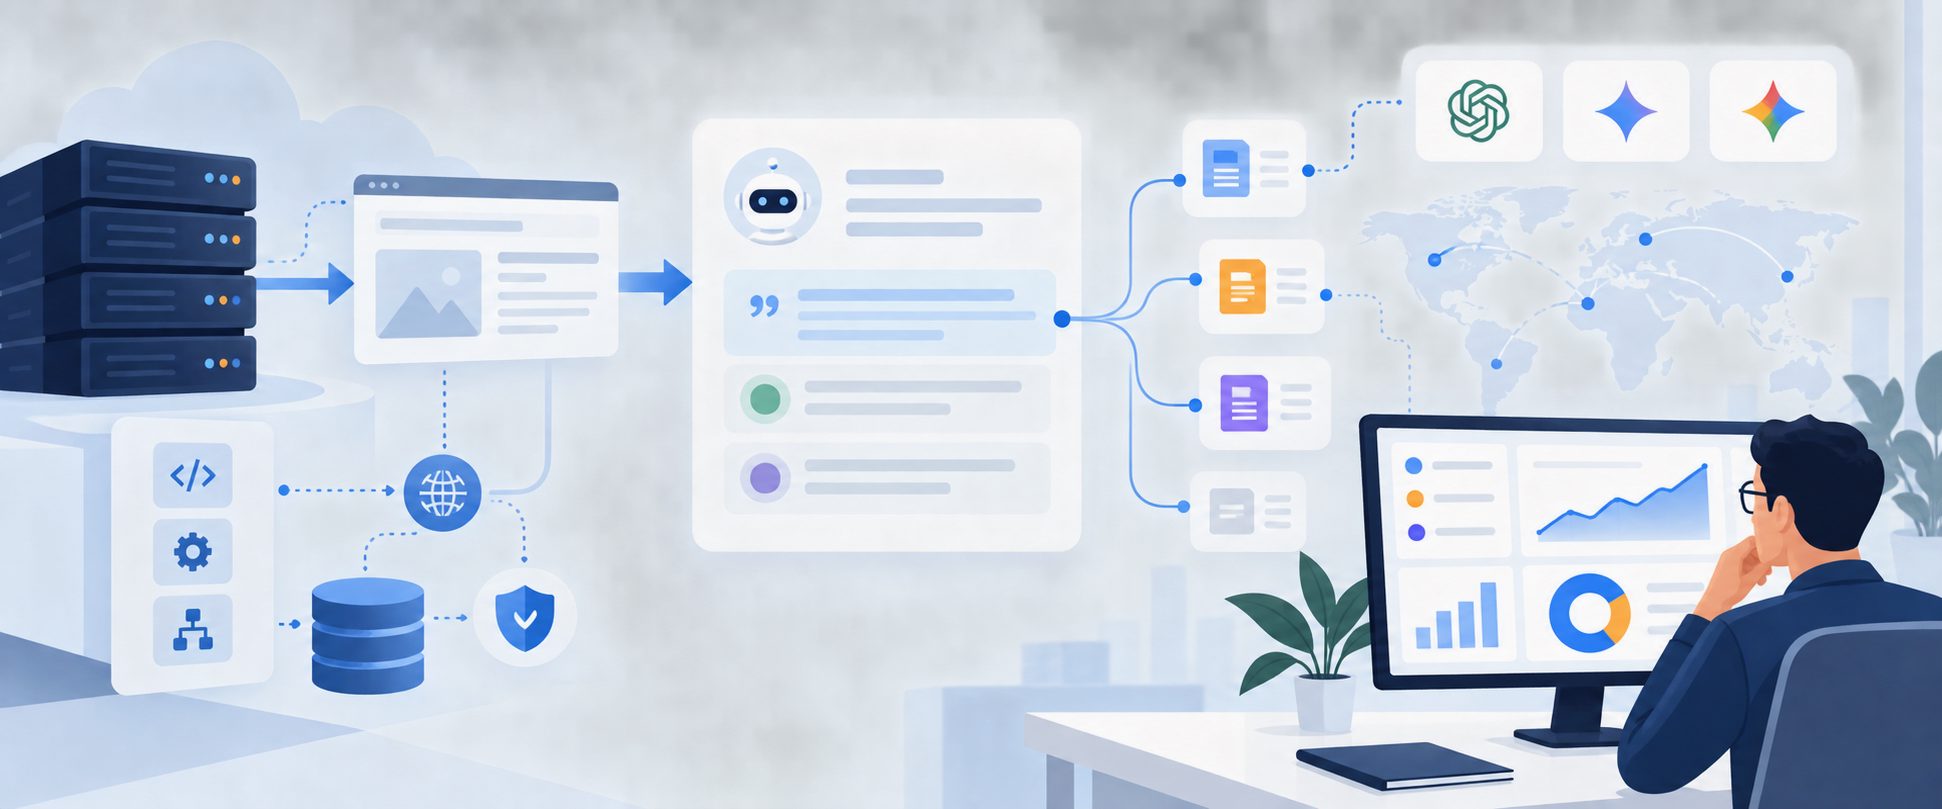
A technical GEO audit for SaaS architecture determines whether AI-assisted search systems can retrieve, render, interpret, and attribute the public facts that explain your product. It focuses on the delivery path between your application stack and a citation—not speculative shortcuts or promises of inclusion.
For SaaS companies, that path often crosses a JavaScript framework, CDN, web application firewall, localization layer, headless CMS, and separate documentation host. One failure can leave buyers with an incomplete product description even when the page looks correct in a browser.
What Should a Technical GEO Audit Examine?
A technical GEO audit should verify five sequential conditions: access, rendering, identity, evidence, and attribution. A page is citation-ready only when its important claims survive every condition in the chain.
This sequence is the Citation-Critical Path, an original framework for separating architectural failures from content problems:
| Gate | Audit question | Typical failure |
|---|---|---|
| Access | Can an anonymous crawler fetch the URL? | WAF challenge, blocked bot, login wall |
| Rendering | Are core facts present without fragile client execution? | Empty app shell, failed API request |
| Identity | Is the product entity unambiguous? | Conflicting names or canonical URLs |
| Evidence | Can claims be verified on the page? | Feature claims without documentation |
| Attribution | Can the system associate evidence with the correct source? | Duplicate URLs, missing authorship |
Score each gate from 0 to 2: 0 means blocked, 1 means inconsistent, and 2 means reliable. Any zero is a release blocker, regardless of the total score. This prevents teams from masking a critical rendering failure with numerous low-impact checklist wins.
For a broader companion review, use the GEO technical readiness checklist for SaaS websites.
How Do You Test JavaScript Rendering?
Test the same URL through four views: the raw HTTP response, a rendered browser, a search-engine renderer, and a text-only extraction. The decisive question is whether the product facts remain consistent across all four.
Google can execute JavaScript, but its documentation notes that rendering has limitations and that not every bot supports JavaScript. Google recommends server-side rendering, static rendering, or hydration instead of dynamic rendering as a long-term workaround. (developers.google.com)
Audit these SaaS elements in the initial or reliably rendered HTML:
- Product name, category, and target customer.
- Core capabilities and use cases.
- Plan or pricing context when publicly displayed.
- Integration, security, and deployment information.
- Links to documentation, comparisons, and proof pages.
Compare the raw source with the final DOM. If essential copy appears only after an API call, consent event, viewport interaction, or authentication check, record it as a rendering dependency. Google’s URL Inspection and Rich Results tools can help verify what its renderer receives. (developers.google.com)
Which SaaS Architecture Patterns Create Citation Risk?
Citation risk rises when public product knowledge inherits application-layer complexity. Marketing pages should not depend on the same state, permissions, or runtime assumptions as the authenticated SaaS product.
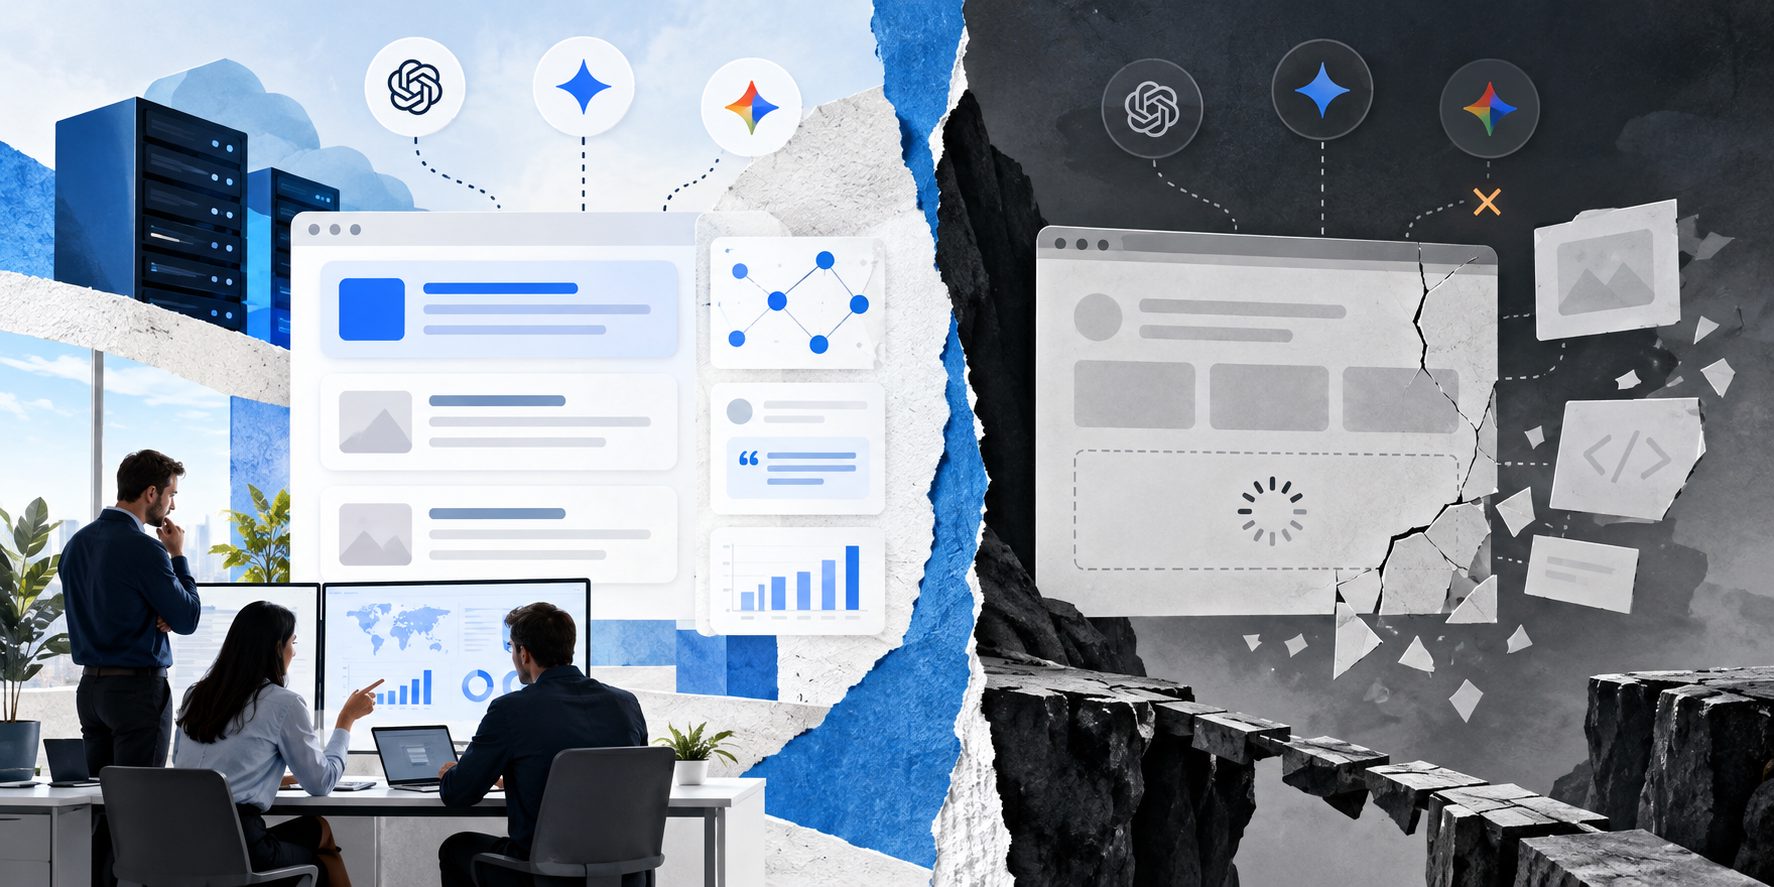
Review these common architectural patterns:
- Single-page application routing: Every public content view needs a stable URL and crawlable
<a>links. Google advises giving each distinct screen its own URL. (developers.google.com) - Headless CMS hydration: Confirm that failed CMS or GraphQL calls do not return a successful but empty page.
- Edge personalization: Test without cookies, geolocation, experiments, or stored sessions.
- Documentation subdomains: Align branding, canonical references, navigation, and sitemap discovery across hosts.
- International routing: Avoid redirecting every anonymous request by IP when a stable locale URL is available.
- Bot mitigation: Inspect CDN and WAF logs for
403,429, CAPTCHA, or JavaScript challenge responses.
OpenAI’s crawler guidance specifically identifies robots rules, WAFs, CDNs, JavaScript challenges, authentication, and geographic controls as possible access barriers. (help.openai.com)
How Should URLs, Canonicals, and Schema Be Audited?
Every public SaaS fact should have one preferred, fetchable URL. Canonicals, internal links, sitemap entries, redirects, structured data, and social metadata should converge on that URL rather than create competing versions.
Google treats redirects, sitemap inclusion, HTTPS, and rel="canonical" annotations as canonicalization signals. Duplicate routes can therefore fragment the source identity attached to product claims. (developers.google.com)
Check for:
- Parameter, trailing-slash, uppercase, locale, and framework route duplicates.
- Canonicals pointing to redirects, blocked pages, or different content.
- Product documentation isolated from the main site’s internal-link graph.
200responses for error, expired, or empty application states.- Structured data that contradicts visible names, dates, authors, or claims.
JSON-LD should reinforce visible evidence, not replace it. Google requires structured data to represent page content accurately and does not guarantee enhanced visibility when markup is valid. (developers.google.com)
Use the schema deployment guide for AI citation optimization to map markup to visible page entities.
How Do You Prioritize Technical GEO Fixes?
Prioritize fixes by citation loss, not by implementation convenience. A blocked product page deserves attention before an optional metadata enhancement because it prevents the underlying evidence from entering the retrieval path.
Use this decision order:
- Restore access: Resolve incorrect robots rules, firewall denials, authentication leaks, and non-success responses.
- Expose primary facts: Move essential descriptions and evidence into reliable HTML output.
- Consolidate identity: Correct redirects, canonicals, duplicate routes, and inconsistent naming.
- Connect evidence: Add crawlable links among product, documentation, security, comparison, and company pages.
- Align machine signals: Make structured data, metadata, sitemaps, and visible content agree.
- Re-test answer behavior: Repeat the same buyer prompts and record mentions, citations, positions, and factual errors.
Google states that eligibility for AI Overviews and AI Mode depends on normal Search indexing and snippet eligibility; it does not require special AI files or unique schema. (developers.google.com) Treat llms.txt as an optional orientation layer, not a substitute for crawlable pages, sound architecture, or indexable evidence.
After deployment, apply a repeatable AI engine position tracking methodology rather than judging success from a single answer.
What Should the Final Audit Deliver?
A useful audit delivers engineering tickets tied to affected URLs, observable failures, expected behavior, and retest instructions. A generic score without evidence is not an implementation plan.
Each finding should include:
- URL and page type.
- Citation-Critical Path gate.
- Raw response status and rendered result.
- Missing or conflicting facts.
- Reproduction conditions, including device, locale, and cookies.
- Recommended owner and remediation.
- A pass/fail acceptance test.
- Buyer prompts used for post-fix validation.
The final report should also separate technical eligibility from observed AI visibility. A technically sound page may still need stronger evidence, clearer positioning, or external corroboration. Conversely, an occasional mention does not prove that the architecture is reliable.
Teams can connect these findings to a wider SaaS generative engine audit methodology or run a free AI visibility diagnostic.
Frequently Asked Questions
Does server-side rendering guarantee an AI citation?
No. Server-side rendering improves reliable access to content, but citation selection also depends on relevance, evidence, source quality, and the answer system’s retrieval process.
Is client-side rendering always bad for SaaS GEO?
No. Client rendering is appropriate for interactive application features. The risk appears when public product facts, documentation, or navigation depend entirely on fragile client execution.
Should a SaaS website create an llms.txt file?
It can serve as an optional summary and resource map. It should not replace standard crawl controls, internal links, stable URLs, visible content, or structured data that matches the page.
How often should the architecture be re-audited?
Re-audit after framework migrations, CMS changes, CDN or WAF updates, domain moves, localization launches, major template releases, or unexplained changes in citations and brand mentions.
What is the fastest technical check?
Fetch a high-value product URL without JavaScript and compare its meaningful text with the browser-rendered page. A large factual gap indicates that rendering deserves immediate investigation.